Exports and evidence
When an auditor, a regulator, or a customer asks how a release was approved, the answer is an attributed, timestamped decision tied to an evidence hash: what was found, what was fixed, what was accepted, on what basis, and who decided. This page explains where each piece is.
For one container
Open the container. The page shows exactly what the reviewer saw: the gates and the verdict, the evidence counts per scanner, each finding with its state and the developer's justification, the reviewer's basis on each accepted risk, and the authorization with the reviewer's identity and the time. The raw scanner output, the pipeline run, and the scans job log open from the evidence panel.
The merge request link opens the durable record in GitLab.
For one reviewer
From the profile menu, Export my decisions produces a list of every decision the signed in reviewer has recorded.
For the portfolio
Security posture shows where the portfolio stands right now. Filter to Authorized for what is currently approved, or to All for every application with its state and who decided it.
For a control mapping
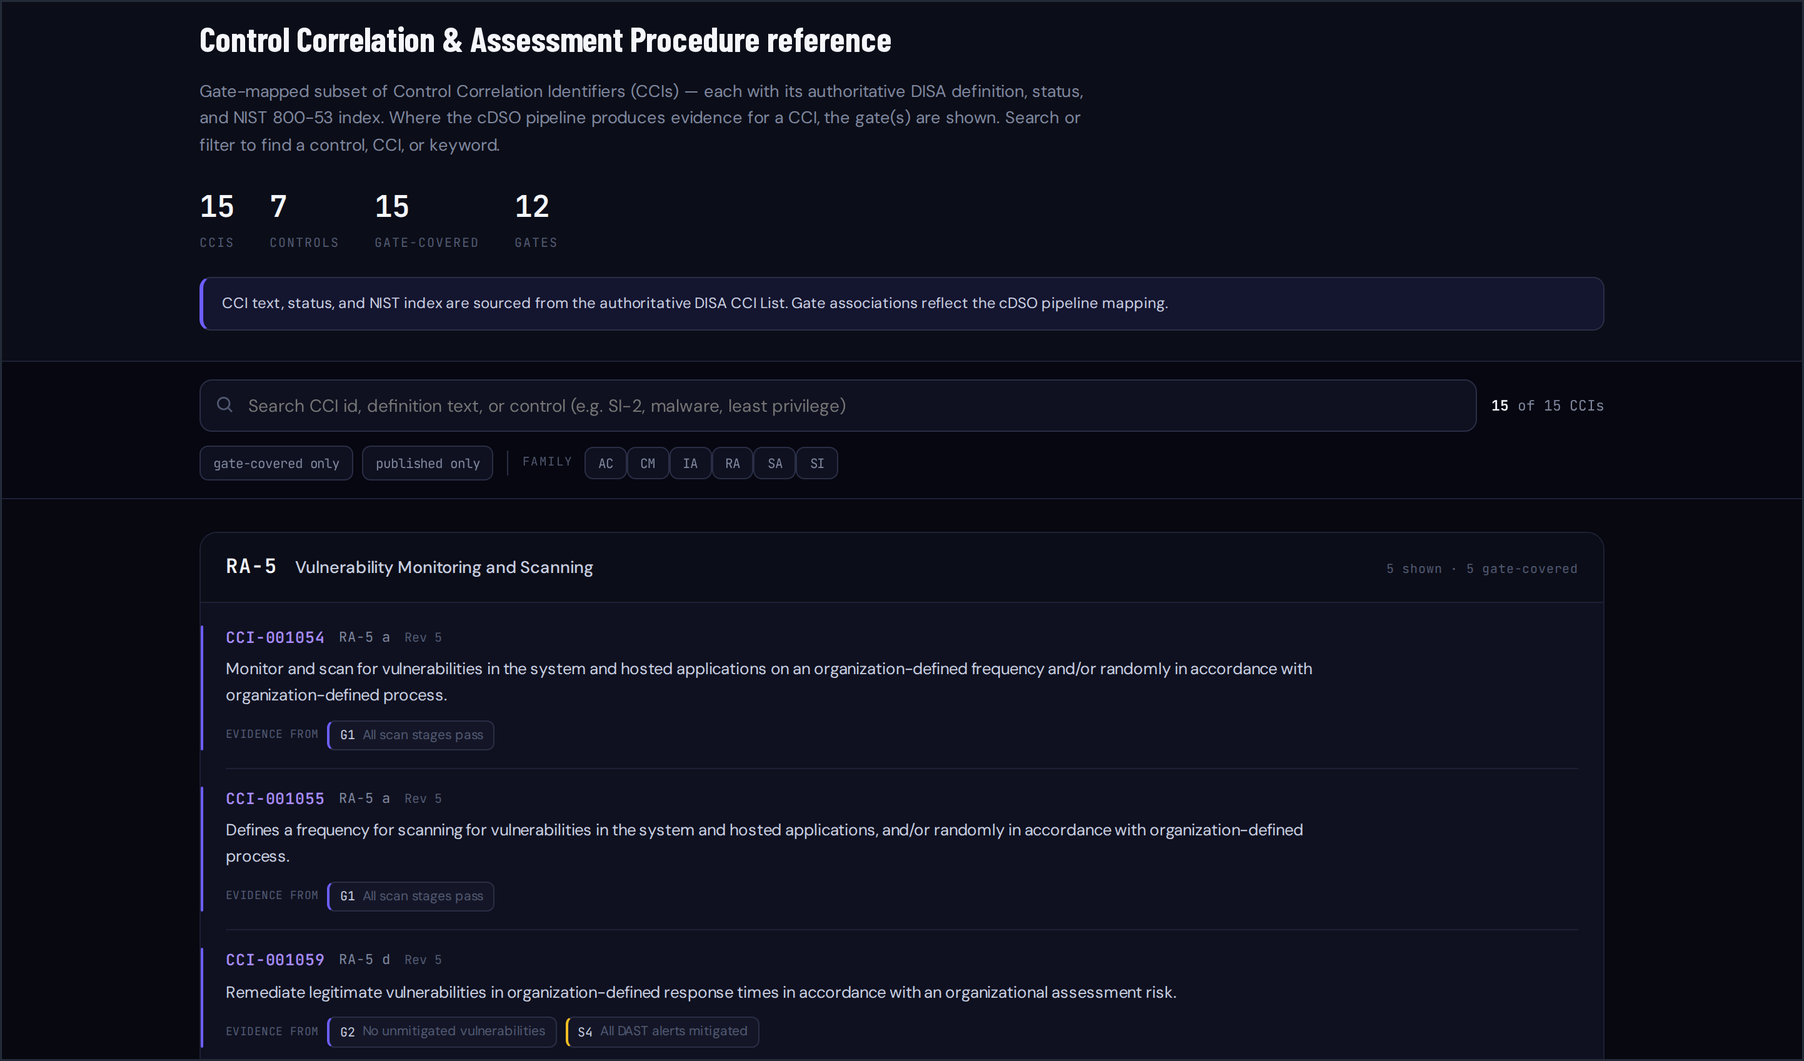
Every gate maps to formal security controls through CCIs. The CCI reference, in the profile menu, lists every control with a description and its NIST 800-53 family, so you can trace a finding to the control it evidences and back again.
Common audit questions and where the answers are
| Question | Where to look |
|---|---|
| What ran against this build? | The pipeline run in the evidence panel, with every stage and job and its outcome. |
| What did it find? | The raw scanner output and the evidence counts. |
| What was fixed? | The delta from the previous run, which lists resolved findings. |
| What was accepted, and why? | The developer's justification and the reviewer's basis, side by side. |
| Who decided? | The reviewer's GitLab identity on the approval. |
| When? | The timestamp on the decision and on the merge request. |
| Against what policy? | The policy version on the decision. |
| Can I check it myself? | Yes. Open the security repository at the evidence hash. |
Formats
The decision log exports as structured data. The merge request, the scan directories, and the justification file are ordinary Git objects and export with the repository. Program deployments can also snapshot the whole bundle to object locked storage at decision time; see Program deployments.
Frameworks
The same record works for a SOC 2 auditor, an ISO 27001 surveillance review, a regulator, or a customer's security questionnaire. Nothing in it is tied to one framework.